Every department wants its own workflow tool, and every tool is another vendor review.
For it and security
Approve it without having to own it.
One platform, isolated per customer in the database, signed in through your identity provider. No custom code for your team to maintain, and a record of every change.
Today
What it looks like now
01
02
Custom-built approval apps become code nobody wants to maintain.
03
Shared platforms raise the question of who else can see your data.
What changes
What you get, and where it shows up
Isolation in the database
Customer data is separated by row-level security in the database, not by application code, and automated tests fail the build on any cross-customer read.
More on thisYour identity provider
Single sign-on over OpenID Connect, with a documented Microsoft Entra setup. No passwords are stored.
More on thisTamper-evident audit
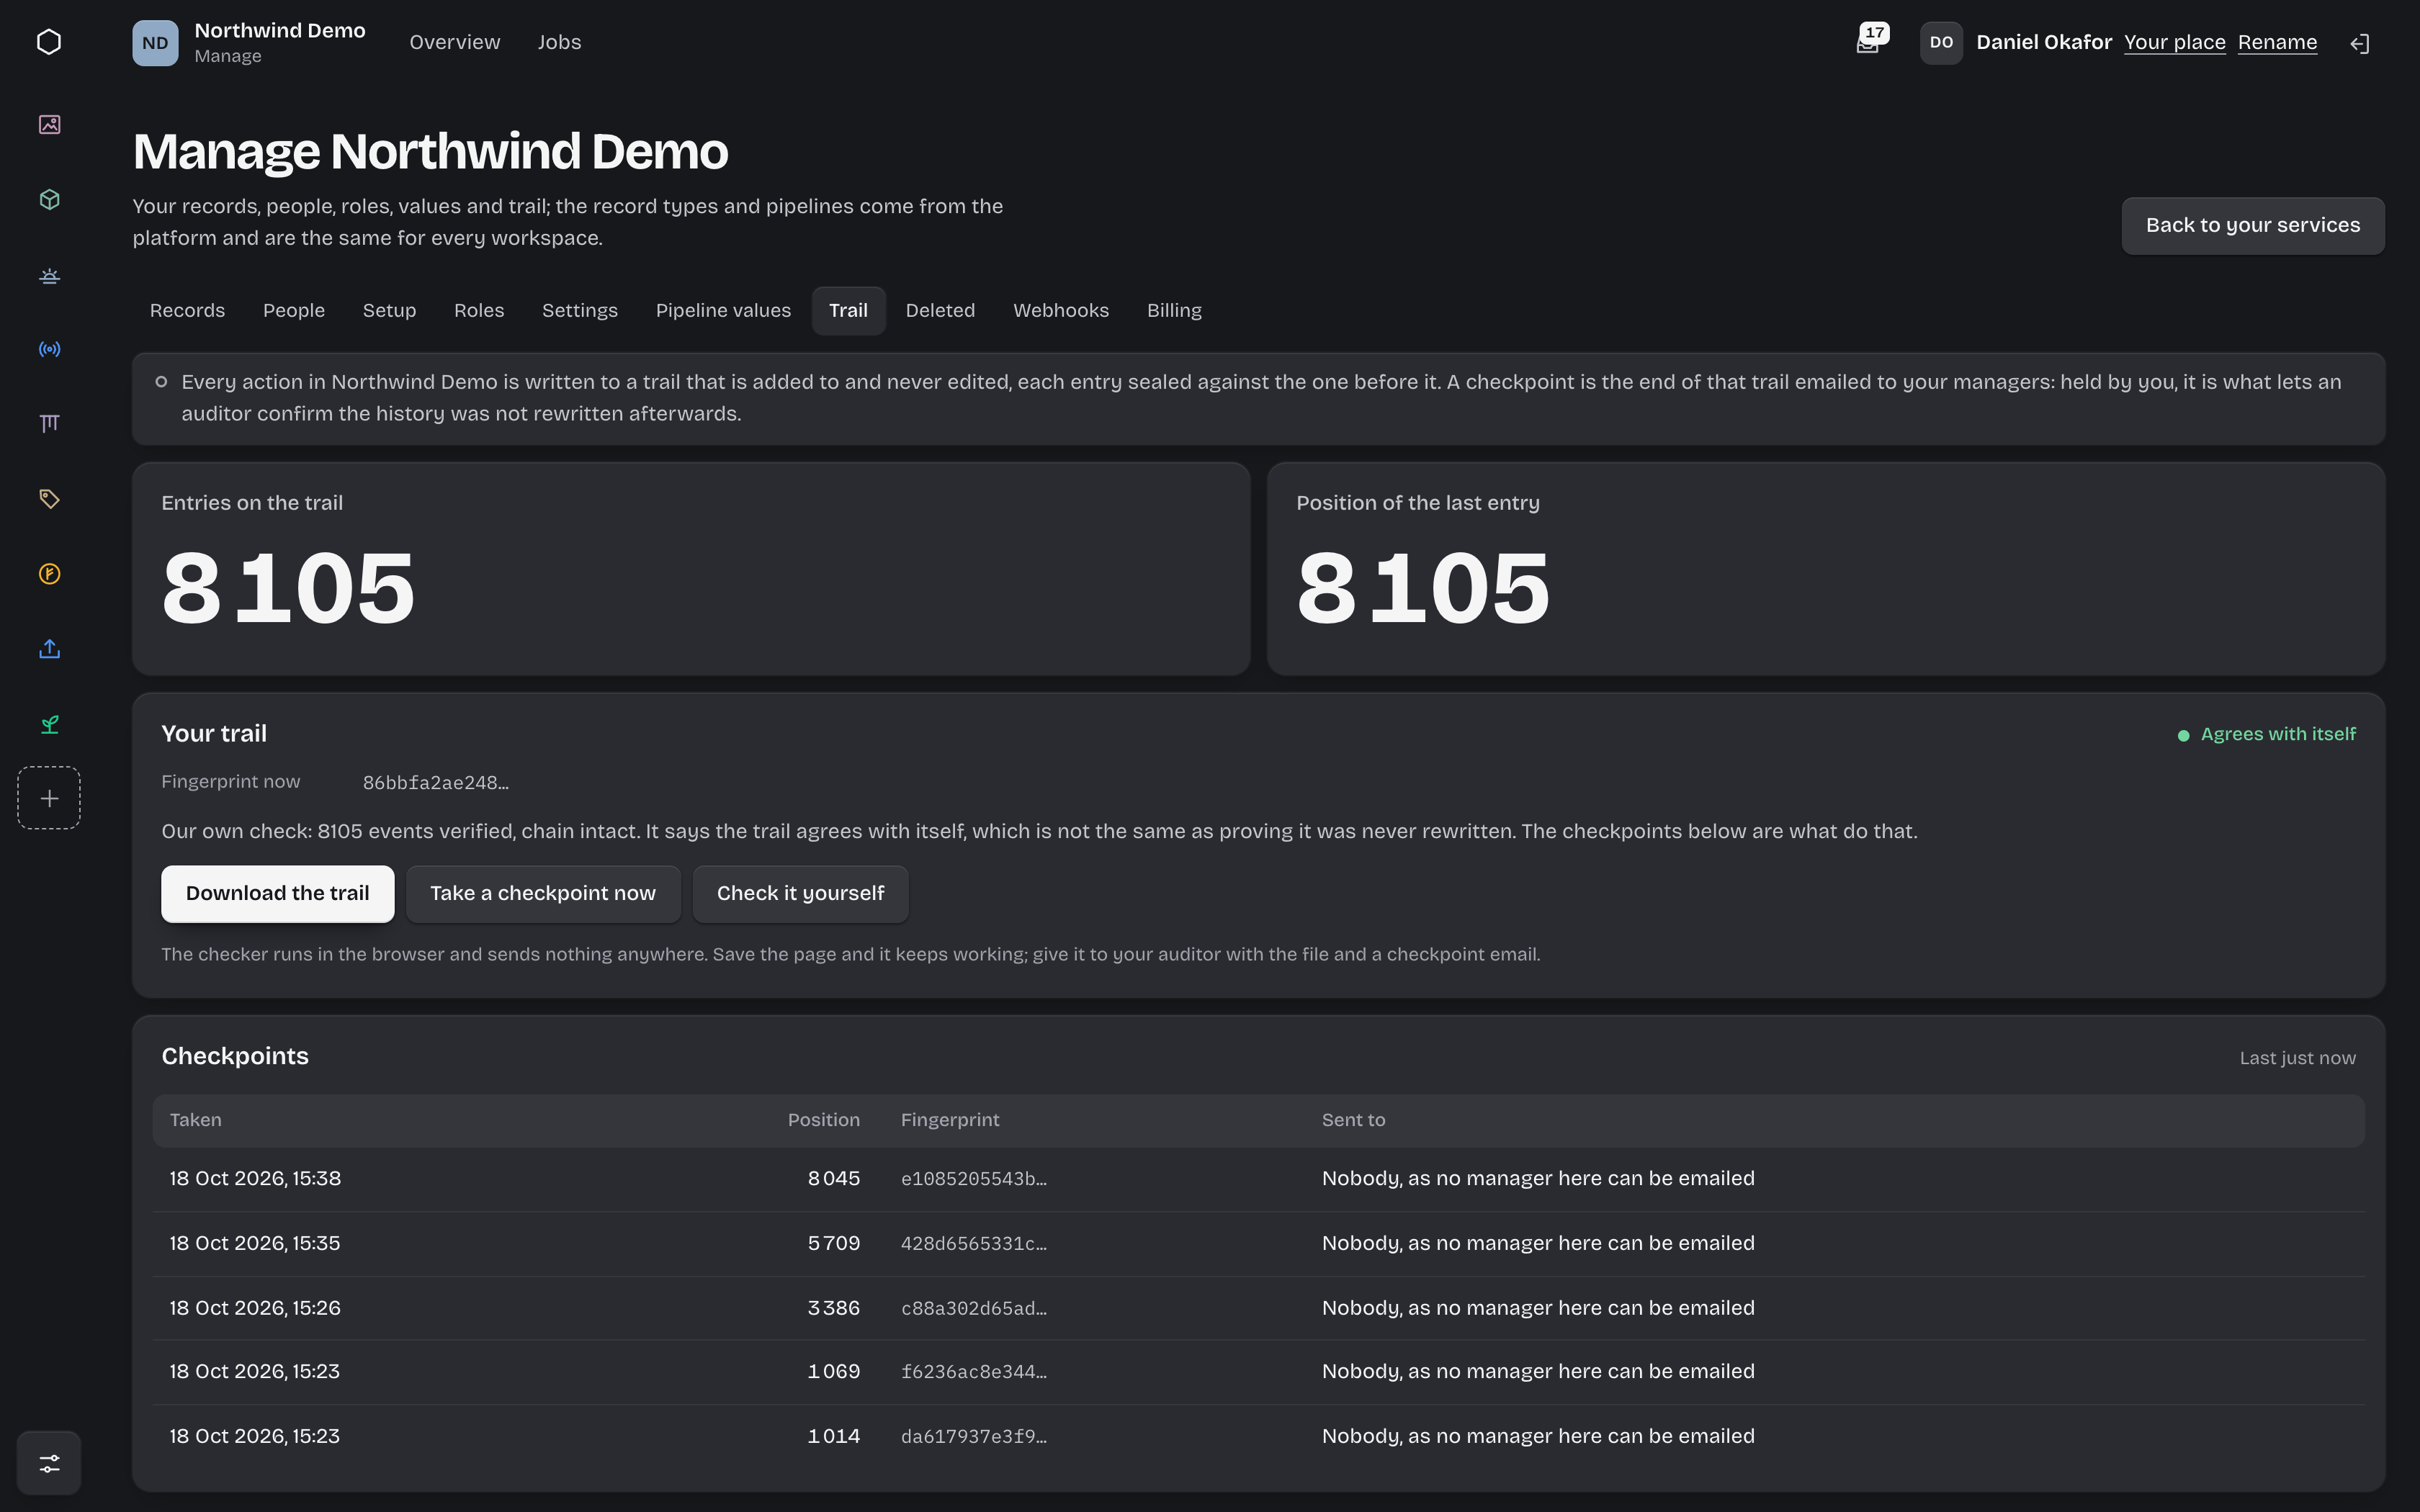
One hash-chained, append-only trail per customer. Configuration changes are on it, with before and after values.
More on thisWhich services
3 of 9Where you work in it
Spend RequestsOperations
Hardware and software spend checked against the budget before it is approved.
AssetsOperationsLaptops and peripherals on a register, with who holds each one and when it is next due a service.
ProjectsProject managementIT work in columns, each move on the same trail as everything else.
Keep exploring
Where to next
Try the Asset Requisitions rule
The rule the service runs, in your browser. No form, no call.
Your process map, running.Branches, thresholds, checks against live records and a designed rejection path. If you can map it, we author it with you as configuration, and Koldheim runs it without a development project in between.
No spend without the right signature.Requests arrive priced from stock, with the department budget in front of the approver. Over your threshold, a second signature is required before anything moves.